SIKUR

Critical asset management aligned with security best practices

REXVOR, in partnership with SIKUR, provides advanced solutions to protect corporate and government data, ensuring privacy and protection against cyber threats.

As integration of systems, equipment and connected devices becomes increasingly necessary, an attack on an operational technology (OT) network or industrial control system (ICS) device may originate in a vulnerability exploited in an information technology (IT) system. Centralised, integrated management of these critical assets significantly reduces cyberattack risks.

The solution enables passwordless authentication using facial or fingerprint biometrics, removing vulnerable credentials and reducing fraud risks.

The SIKUR Connect platform enables effective access management for OT and ICS systems, eliminating reliance on VPNs, reducing costs and enabling these systems to be removed from the public Internet for greater security.

Based on industry best practices, the solution references the General Data Protection Regulation (GDPR, 2016), the US IoT Cybersecurity Improvement Act (2020), and the UK consumer IoT security code of practice.
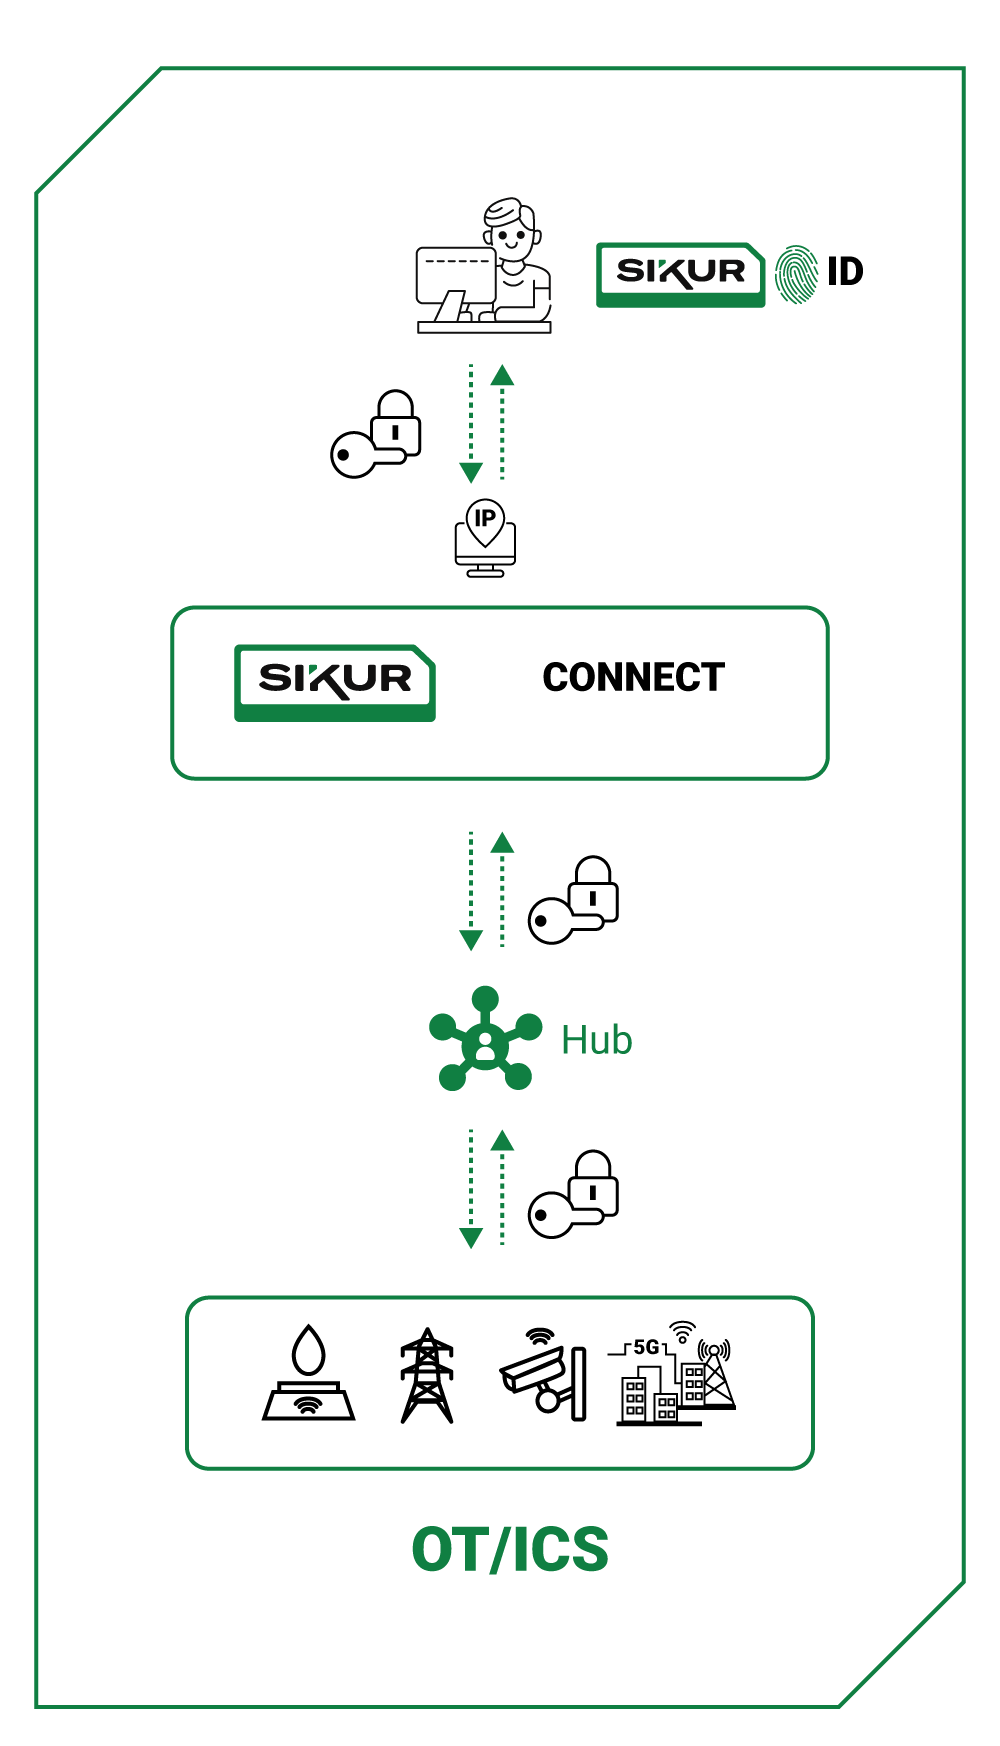
Centralised access and critical asset management with SIKUR

Key features

Contact us

Identity management

Allows users to access authorised devices without knowing credentials.

Passwordless authentication

Provides secure platform access without passwords, helping prevent fraud.

Audit and compliance

Records event logs, keystrokes and session videos for audits aligned with international standards.

Secure data collection and storage

Protects and securely stores device data.

Secure reverse tunnel

Enables secure device access through encrypted tunnels, reducing operating costs.

Zero Touch

Simplifies remote device deployment and provisioning without physical contact.

Device management

Secures access and updates and helps protect against equipment theft.

No default passwords

Replaces passwords with private keys on IoT devices, aligned with security requirements.

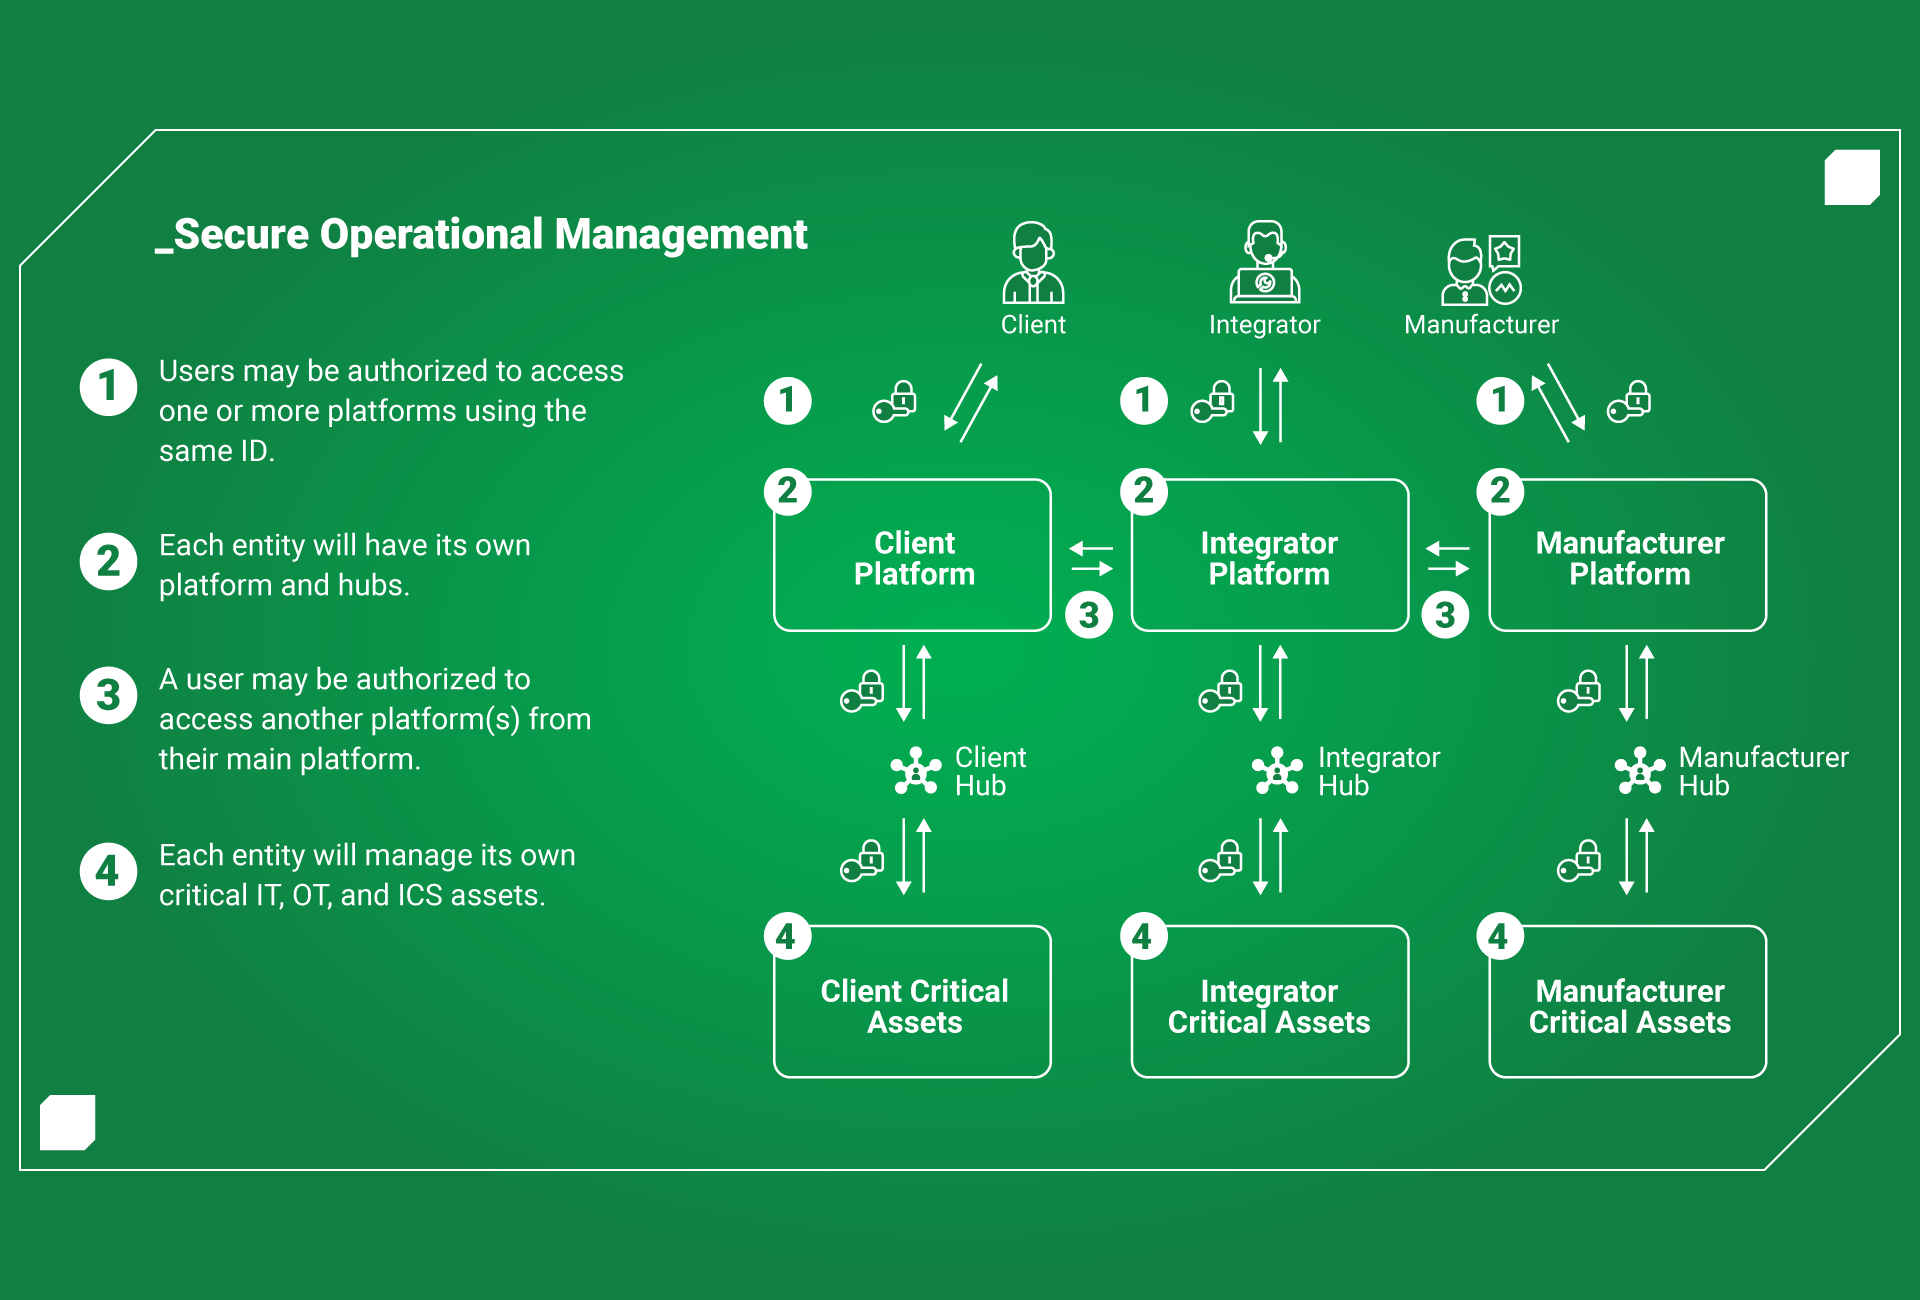
_Secure operational management

  1. Users can be authorised to access one or more platforms with the same ID.
  2. Each entity has its own platform and hubs.
  3. A user can be authorised to access other platforms from their main platform.
  4. Each entity manages its critical IT, OT and ICS assets.
Customer, integrator and manufacturer: a single identity, interconnected platforms, hubs and critical assets with protected connections and access control.

How can we help?

Access management policy aligned with international best practices

Elimination of credential use by employees and supply chain partners accessing OT and ICS systems

Centralised access authorisation and revocation

Removal of VPN requirements, reducing risks and operating costs